
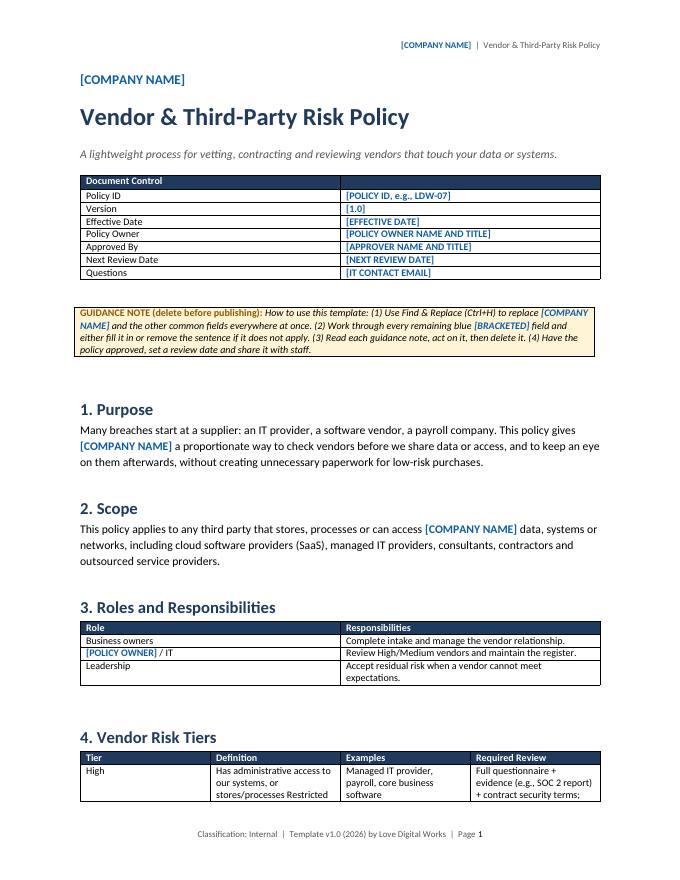
Vendor & Third-Party Risk Management Policy Template
A lightweight process for vetting, contracting and reviewing vendors that touch your data or systems.
- Editable Word (.docx) + PDF
- Fill-in [BRACKETED] fields and guidance notes
- Approval page, staff acknowledgment and revision history
- Written for businesses with 5 to 100 employees
Why a small business needs a vendor risk policy
Many breaches start at a supplier. This policy gives you a proportionate process, with a deeper look at high-risk vendors and no paperwork for low-risk purchases.
What's inside this vendor risk management policy template
Besides the standard purpose, scope, roles, exceptions, enforcement and review sections, this template covers:
- Vendor Risk Tiers
- Before Engaging a Vendor
- Minimum Security Expectations
- Contract Requirements
- Ongoing Management
- Appendix A: Vendor Intake Questions
- Appendix B: Vendor Register
Guidance notes explain the choices to make, for example which settings an insurer may ask about. Delete them before publishing. This template is not legal advice and does not certify compliance with any standard.
This policy is also included in the Complete Bundle ($79) with all 10 policies and both spreadsheets.
How it works
- Buy securely through Stripe checkout.
- Download instantly from your private download page.
- Open in Word or Google Docs and replace [COMPANY NAME] and the other fields.
- Follow the guidance notes, get approval and share with staff.
Related templates
Acceptable Use
Sets clear rules for how employees may use company devices, accounts, networks and data.
Password & MFA
Defines modern password rules and where multi-factor authentication is mandatory.
Incident Response Plan
A step-by-step plan for detecting, containing and recovering from security incidents, with contact lists and checklists.